

Where cybercriminals used to be present in a target’s network for weeks or even several months before visibly striking, today that is almost never longer than six days. This is because the entire ecosystem behind cybercrime has changed drastically.
Today, attackers are present in their target’s network for four to a maximum of six days. This is according to Geert Baudewijns, CEO and founder of Secutec, ahead of the CyberNova conference in Antwerp. “Just two years ago, it was still a matter of weeks, but today there are few cases where they remain in the network for longer than six days.”
Rapid evolution
The modus operandi of cybercriminals has thus evolved significantly in a very short time. In 2022, it was still normal for attackers to have access to a corporate network for about three months, after which they announced their presence themselves by releasing ransomware. They used that time to map the network, move laterally, gain additional access, and exfiltrate interesting data. Only then did the encryption start, followed by a demand for ransom.
That has completely changed today, Baudewijns observes from his expertise as a negotiator with cybercriminals in cases of extortion. The cause lies in a fundamental shift in the ecosystem of the attackers themselves.
Fragmented landscape
“The ransomware landscape consists of different organizations with specialized roles, all working together,” he says. “There are professional hackers, programmers who create ransomware platforms, negotiators, and criminals who make use of all those services.”
It is therefore not the case that one gang breaks in, develops ransomware, steals data, and encrypts PCs: the criminals who break in are not the same as those who build ransomware tools. Access to a network and ransomware-as-a-service are both sold and bought by parties who then get to work with them.
Less loyalty
That was already the case a few years ago, but the dynamics were different. Back then, hackers sold access to a ransomware collective with an initial (low) cost and the promise of, for example, twenty percent of the profit if the target paid. The attackers who sold the initial access to networks were quite loyal to the ransomware gangs.
“Today, that loyalty has disappeared,” Baudewijns observes. “Initial access is often sold multiple times to different ransomware gangs. The profit for the sellers no longer necessarily comes from a percentage of the ransom, but from the sale of access and tools.”
Race against other criminals
The result of this is that gangs are generally no longer guaranteed to be the only ones present in their target’s network. Whoever encrypts data first can demand a ransom. That is why they immediately start exfiltrating data, which has meanwhile become the main goal of the attack. After only about four days, the ransomware payload is released. Waiting longer carries the risk for the gangs that a competitor will beat them to it.
“After the payload is deployed and the ransom demand is on the table, the hackers disappear from the network,” Baudewijns knows. “They will never take the risk of staying present any longer.”
The fear of competition is not the only motivator to work faster. Better detection at targets also plays a role. The longer criminals are present in the network, the greater the chance they will actually be discovered.
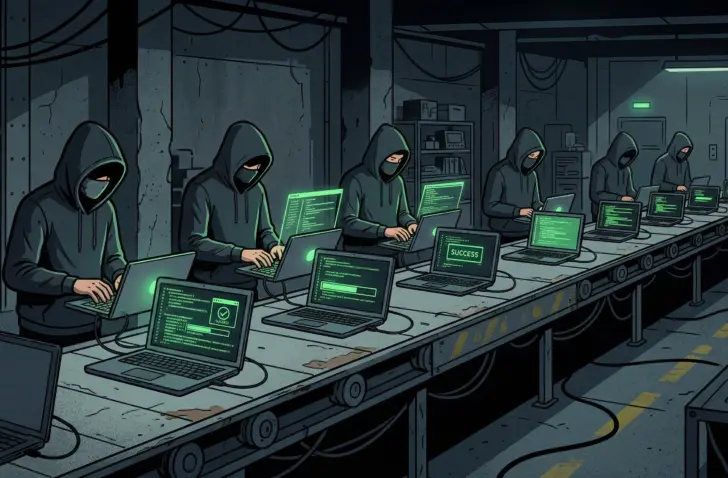
That is why ransomware and data theft are more than ever assembly line work. “Ransomware gangs only buy access to a victim’s network the moment they have someone available to get to work with it immediately,” says Baudewijns.
Focus on the SME
With that new reality in mind, the profile of favorite targets has changed. The world’s largest companies are no longer the most relevant victims for gangs. They have complex and segmented networks with more advanced security.
Baudewijns: “Companies with ten to 500 seats with a flat network topology are in the sweet spot.” In other words, it is SMEs that are primarily being targeted today.
All of this changes the way organizations need to protect themselves. Attackers do not target specific companies but buy access wherever they can get it. Reducing visibility on the internet and ensuring you are not an easy target is the most important way to protect yourself. Best practices still apply: good hygiene, two-factor authentication, and especially patching quickly are all steps in the right direction.