


Hacker collective ShinyHunters has stolen data from more than 100 organizations via the vulnerability in Oracle PeopleSoft. The breach reportedly involves 429,000 files.
The hacker group ShinyHunters claims to have stolen more than 297 GB of data from the Council of Europe by exploiting a zero-day vulnerability in Oracle PeopleSoft. The haul includes corporate data, CVs, and employees’ medical records. A hundred other organizations, including the University of Nottingham, were also affected.
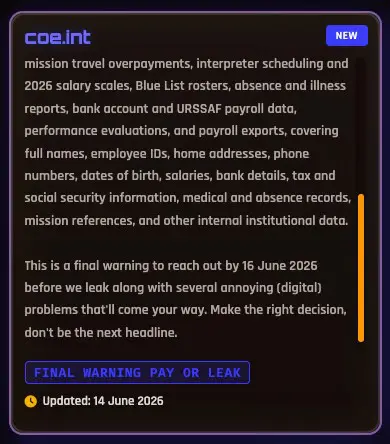
The Council of Europe confirms it is launching an investigation into the breach but declined to comment further. ShinyHunters is exploiting vulnerability CVE-2026-35273, which according to Google was actively exploited between May 27 and June 9. The tech giant warned more than 100 organizations worldwide, primarily in the US and the higher education sector.
Zero-day vulnerability affects organizations worldwide
According to ShinyHunters, they have compromised more than 100 organizations via 300 vulnerable PeopleSoft instances. In addition to the Council of Europe and the University of Nottingham, where data from 454,600 students was leaked, other educational institutions were also targeted. Google confirmed that 68 percent of the affected organizations operate in higher education.
Additionally, the group previously targeted Instructure, the creator of the Canvas learning platform, earlier this year. Data from 275 million students and employees was stolen there. Instructure reportedly reached a settlement with ShinyHunters, which in practice amounts to paying ransom.
Previous attacks on the education sector
In March, ShinyHunters already claimed to have stolen data from Infinite Campus, a provider of K-12 education software. At the time, Infinite Campus refused to pay, after which the group published 137,000 email addresses and other personal data. Infinite Campus stated that the leaked files primarily contained names and contact details of school staff.