

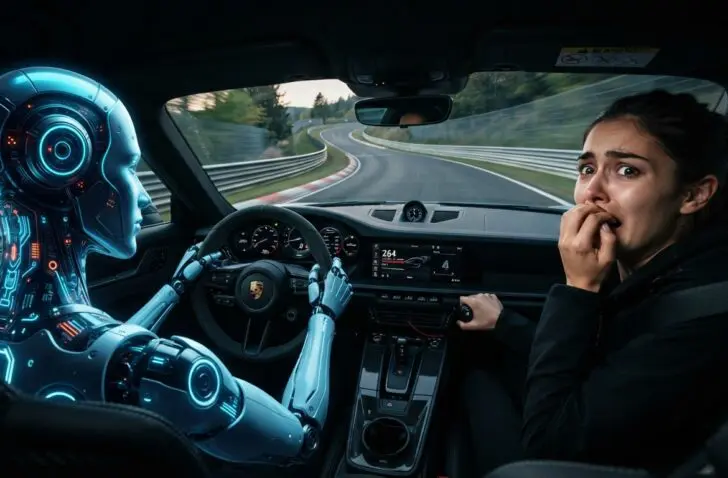
Attackers exploit vulnerabilities before they are even known, and companies roll out AI without knowing what it does. Experts are searching for the brakes for AI in cybersecurity.
“In the past, you had days until a vulnerability was exploited. You could fix a vulnerability and only then make it public. Today, we speak in ‘negative days’: attackers exploit vulnerabilities before you can patch them because they have access to the same AI models.”
The tone is set by Satish Balakrishnan, VP and GM at Red Hat Ansible. Together with Ron Mukherjee, cybersecurity consultant at ESET; Olivier Menil, Strategic Advisor BeLux at Fortinet; Kris Spruyt, Senior Business Consultant at Telenet Business; Maarten Bovée, CEO of NTX; and Ulrich Seldeslachts, CEO of LSEC, he discusses the impact of AI and security at the ITdaily roundtable.
Experts see AI as both a useful tool and a threat to defenders. AI increases speed, but the technology’s brakes have not yet been sufficiently tested.
Security by design: finally relevant?
Kris Spruyt takes a step back and focuses on what he considers an underestimated link in security: the human element. “We often talk about robots, software, AI, you name it. But the human aspect within your organization is just as important, sometimes even more so. People need to be trained and made aware of NIS2 regulations, as they also play a vital role in the whole.”
“If you don’t address that awareness through training, you can do a lot in terms of products and processes, but you still leave yourself exposed,” says Spruyt. Balakrishnan agrees. “If the mindset that automation is business-critical is missing in the organization, people won’t be incentivized.”
“Problems arise because people didn’t understand what was happening, it’s as simple as that,” Olivier Menil chimes in. He believes security vendors need to look in the mirror: “I don’t know how many years each of you has been talking about security by design here. We’ve been doing that for a long time, with actually very little traction.”
“AI will be the trigger. The time to discover problems is shortening. AI creates an asymmetry that we are all victims of. I think AI will become the lever for security by design in that regard.” Seldeslachts points to regulation. “There too, European legislation such as the Cyber Resilience Act mandates that products be developed according to security by design.”
Vendors under pressure
Ron Mukherjee sees his own sector changing under the impulse of AI. “As a vendor, we notice that the entire organization is changing profoundly at all levels. Think of pricing models and the way we go to market. We can no longer sustain that, because at a certain point the price becomes so low that it’s cheaper to do it yourself.”
“This is truly a complete shift in our world,” Mukherjee asserts. “As a company, we are now putting all focus on AI. We are essentially becoming a full AI company. If I want to, I can build a CRM tool with AI in a weekend.”
Balakrishnan disagrees. “It will put pressure on your costs, but I think the risk of replacement is very small. Building a proof of concept with AI is very easy. Bringing it into production and being able to maintain it continuously is something else entirely.”
“Today we use AI for our development,” says Balakrishnan. “Of a product we released two or three weeks ago, 99 percent was built by AI. But a lot of human work is needed to validate everything and to check if it’s scalable. You can build a very good application, but can you also roll it out to thousands of other companies?”
“That validation is now also largely done by AI. No human can do this so quickly, but that doesn’t mean it’s always better with AI,” Seldeslachts notes.
Building a proof of concept with AI is very easy. Bringing it into production and being able to maintain it continuously is something else entirely.
Satish Balakrishnan, VP & GM at Red Hat Ansible
A car without brakes
The panel becomes much more cautious when asked to look ahead. Will there be a moment when AI does become better? “That’s really hard to predict,” says Maarten Bovée. “The price to build things might go down, but it also drives innovation and new things at an accelerated pace. As an MSP, we have to automate like crazy today, because several patches and critical alerts come out every week. You didn’t have that in the past.”
“In the past, you really had to be an experienced hacker to pull off something crazy,” Bovée continues. “Now you can have an agent hack and perform multiple supply chain attacks. There are ungoverned LLMs you can find on the dark web for five dollars. Our customers, small and large, need automation, lightning fast. It has to be faster and cheaper. For us, building governance at our customers is also very important. What happens with shadow AI?”
According to Mukherjee, governance should not stop innovation. “Perhaps you can see AI within governance as a user.” Bovée follows. “That’s how you should look at agents. They can handle and execute things for you. But I would still call them ‘dumb computers’.”
Dumb Ferrari
“What is AI in IT today?” Menil poses a philosophical question. “A dumb tool with insane capabilities and an execution speed that is out of proportion. Problems arise because we add new capabilities to it every day without control. It’s like having a car and putting extra power in it. What is the top speed? We don’t know. Are the brakes good enough? We don’t know that either.”
“And humans aren’t following today, aren’t checking. It’s very good for the media. But in an air-gapped environment, there is no risk of an agent connecting to the internet. If you let a default gateway run to the internet, then of course there is.”
SMEs in particular shouldn’t want to drive the fastest car, Bovée believes. “In the US, they’re holding a race that I think is even stupid. Most of our customers, even the large ones, ask for simple automation. They don’t need the latest exclusive Ferrari model.”
AI in IT is a car whose top speed is unknown, and whose brakes have not been tested.
Olivier Menil, Strategic Advisor BeLux Fortinet
Same mistakes
“We’ve been building in AI components for almost a year, and we’ve regulated it internally within the company,” Spruyt says of the approach at Telenet. “From personal AI to fully industrialized AI agents: we’ve built governance around that. As an individual, you can use AI. We’ve integrated all available elements into Copilot, but everything runs on one tenant, one closed environment.”
“If you want to build something specific that can help a department or the whole company, you have to go through a governance body. If you don’t, you can’t roll anything out. It’s essentially an authorization board that gives you access to certain capabilities and to data sources that are normally not allowed. With that authorization, you also get the tools and support to develop agents. It’s fully regulated,” he explains.
“That sounds logical, but how sure are you that AI can’t escape?” Seldeslachts reacts. “What I see many companies doing today reminds me strongly of cloud innovation fifteen years ago. The same models are being applied, and I see the same mistakes being made again. Those cost organizations millions of euros.”
“We’ve talked a lot about generative AI, but not about AI in IT operations. That is precisely what’s most important,” Balakrishnan takes over. “If your agent deletes a database, you and not the AI agent are responsible for that. So you have to be extremely careful and put governance around agents.”
According to Balakrishnan, automation must be implemented end-to-end. “Without that, AI doesn’t understand the context. Then a gap arises between companies that have automated and companies that cannot. AI is very good at exposing new incidents and making suggestions. But you don’t want those suggestions to be executed in IT operations without a human in the loop. LLMs will hallucinate and make things up.”
I see companies making the same mistakes with AI as with cloud, and those mistakes cost millions of euros.
Ulrich Seldeslachts, CEO LSEC
Same rights as the CEO
That’s why companies need to start thinking about how they secure their data,” Bovée chimes in again. “AI agents are being rolled out with the same rights as the CEO or the IT manager. Before you know it, you’ve deleted all your emails or your entire SharePoint. Or you change data in a database, and then you no longer know what your original data was.”
According to Menil, the focus of security must shift to data and identity. “We are moving away from historical network security. When I ask customers using AI today how they control it, they have no idea. They roll it out and get a result, but they don’t know what’s happening behind the scenes. Meanwhile, we continue to fight in a very traditional way, project by project.”
“To boost maturity, MSSPs have a major role to play, because vendors cannot scale. Not even the big players. My favorite slide consists of six letters: AI vs IA, artificial intelligence versus intelligent automation. I think we are already in the second phase today.”
Compliance the basis, resilience the goal
The experts don’t want companies to be deterred by AI; on the contrary. “Use it for your security,” Seldeslachts advises. “An important part of the NIS2 requirements is good management, including having policies and guidelines in place.”
“SMEs don’t know where to start and what should be in them. This is a perfect start: write me twenty rules regarding cybersecurity policy that I can give to my ten employees. The clearest policy texts I’ve read were written in less than five minutes thanks to AI. With limited human support to proofread them or change emphases, that gives SMEs a level of leverage we’ve never seen before,” Seldeslachts says positively.
Balakrishnan sees AI as a way to address staff shortages. “Many SMEs have one IT person who has to follow up on everything. How are they also supposed to handle security? They need agents that can do the work. But you have to be very careful about which agents you deploy, because they can do the wrong thing.”
For now, the experts are looking for brakes in governance and in a human who approves AI suggestions. No one at the table dares to predict how fast AI will evolve in the meantime. “It’s hard to predict where we will be in six months or a year, in terms of capabilities and vulnerabilities, as well as how AI will change our business model. Regulation makes us safer,” says Spruyt.
“We have better structure, visibility, and tools. In terms of AI, it’s more important to govern than to spread fear or stop innovation,” Mukherjee concludes. “In summary, I would say: compliance is the basis, but resilience is the goal.”
Compliance is the basis, resilience the goal.
Ron Mukherjee, cybersecurity consultant ESET